

/platform/credentials) is the second tab of the Vendors sidebar entry,
next to Vendors. A person who may read credentials but not vendors
sees it as its own Credentials entry. It is the credential registry: what Forge can
authenticate to, grouped by vendor and connection, for whom, and whether each credential is proven
against the live provider. Credential approvals are part of this page — the Needs review count
and filter hold every pending credential. The old /trust-fabric/credential-approvals and
/trust-fabric/credentials/approvals URLs redirect to the registry filtered to pending credentials.
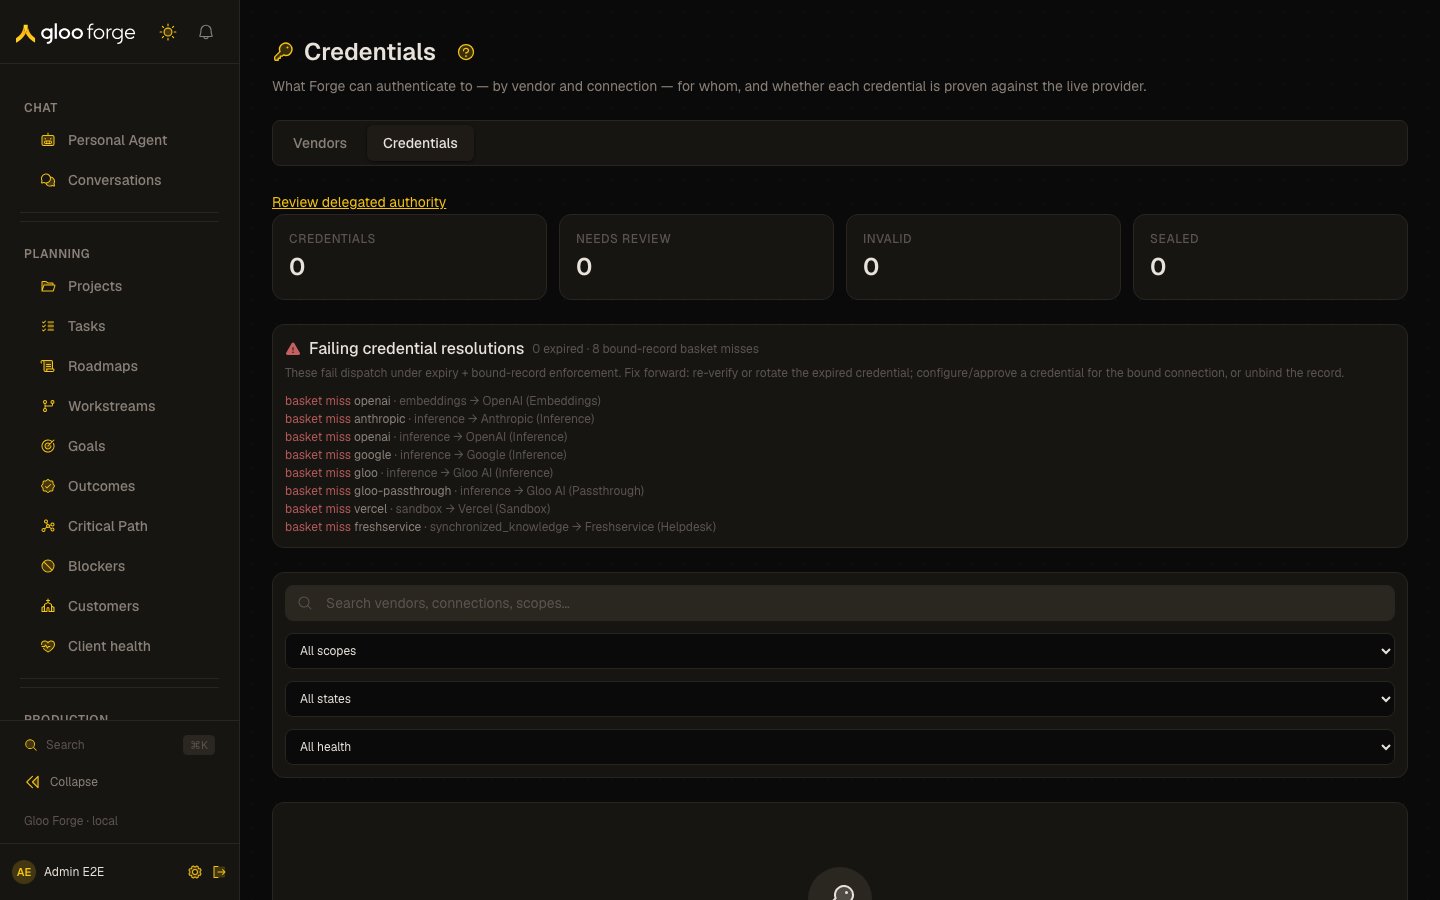
Credentials — Forge Console at /platform/credentials
What you can do
- Filter to Needs review to triage pending credentials, then approve or reject each one from its detail drawer.
- Open a credential to see its identity, resolution story, trust and proof, and what uses it.
- Run Verify now against the live provider, share a credential down to descendants or seal it, or revoke it with a review note.
Who can act
Each Credential action checks one permission at the Credential’s own scope. A company grant covers that company and its descendants; a platform grant covers every Credential, including system ones. A Credential whose company can’t be resolved is refused to everyone and left out of the registry.
Verify now runs a live, authenticated probe with the real secret and records its outcome, so it is a write: verify requires
credentials:write at the Credential’s scope (admission credentials:read), the button needs both, and a Forge agent cannot run it.
You cannot approve a Credential you requested. A Credential still scoped to an agent, user, role,
position, project or factory shows Platform administration required until scope migration: only
a platform grant administers it until those rows move to a company or system scope.
Credential creation, rotation, sharing, deletion, approval, rejection, revocation and live
verification each write an audit event. Audit detail includes lifecycle metadata such as target,
scope, approval state and field names, but never a field value, secret id, OAuth token or client
secret.
Key state to watch
- Needs review — the count of credentials waiting for an approve or reject decision.
- Blast radius — the Used by section shows what depends on a credential before you revoke or seal it.
Review delegated authority
Review delegated authority opens Trust Fabric → Access → Delegation at/trust-fabric/access/delegation. Credential management stays in Platform. The separate bounded
grant preview needs grants:read, with grants:manage for confirmed per-version revocation.
See Access for the limits and current-authorization distinction.
Related surfaces
- Vendors: the vendors and connections a credential authenticates to.
- Vaults: where secret values are stored.
- Access delegation: authority delegated to a credential.
- Connections: your own account’s external connections.